
How to Map BAA Flow-Down Across Your SaaS Stack Without Missing a Subprocessor
A signed BAA with your customer is the start, not the finish. Here is how to trace every subprocessor that touches PHI across your stack and close the gaps auditors look for.
The 7 HIPAA Compliance Gaps That Catch SaaS Healthcare Startups in Year One
Most digital health startups find out about their HIPAA gaps from a customer’s security questionnaire, not their own checklist. Here are the seven that surface first, and how to close each one.
CMMC Phase 2 Is 5 Months Away: The Subcontractor Triage Checklist
CMMC Phase 2 begins November 10, 2026. The 6-question triage checklist for DoD subcontractors who need to be audit-ready before the C3PAO window closes.
How to Choose SOC 2 Compliance Software for a SaaS Startup: Vanta vs Drata
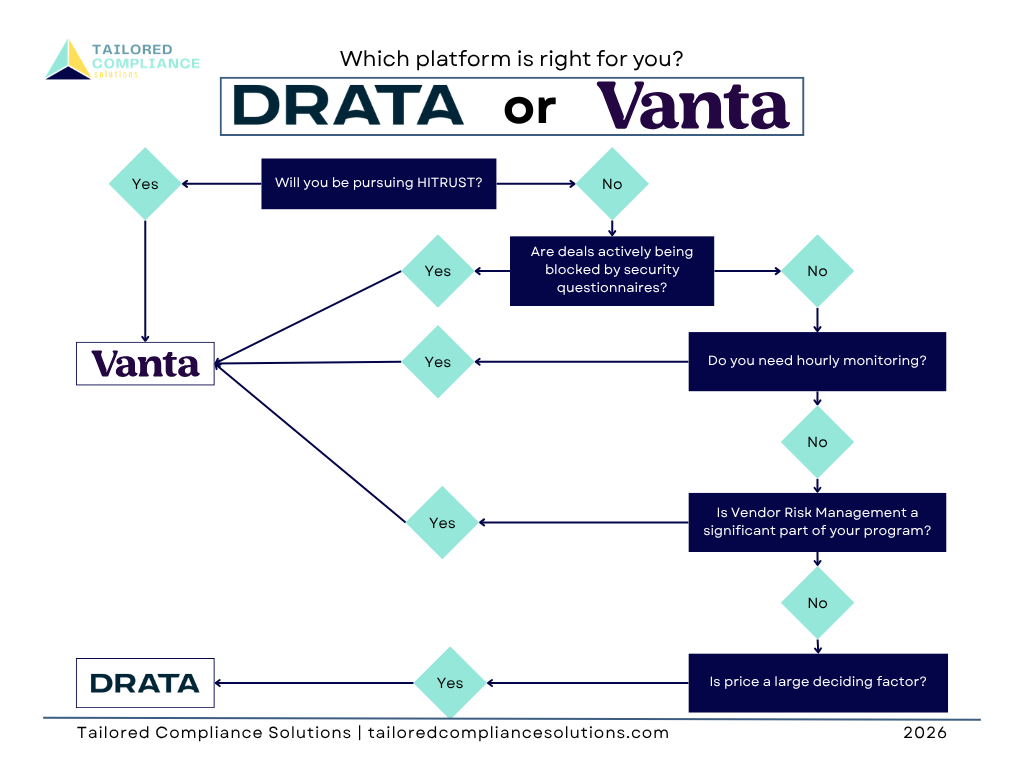
Vanta vs Drata for SaaS? Both produce equivalent SOC 2 outcomes. The right choice depends on your specific situation. Here's the honest decision framework.
How to Reduce SOC 2 Compliance Costs for SaaS Companies (Without Cutting Corners)
SOC 2 is expensive, but most SaaS companies overspend by $30K+ on the wrong things. Here's where the money actually goes and how to lower each line item without gutting quality.
Vendor Risk Management for SaaS Companies: The SOC 2 Control Most Teams Ignore Until It's Too Late
Vendor risk management is the SOC 2 control most SaaS teams underestimate. Here's what CC9.2 actually requires, where evidence breaks down, and how to build a program that holds up under audit scrutiny.
What Is an ISMS and Why ISO 27001 Requires More Than a Policy Library
An ISMS is more than a policy library. ISO 27001 requires a living system of governance, risk management, and continuous improvement. Here's what that actually means to build and maintain.
Security Logging and Monitoring for SaaS: What SOC 2 and CMMC Both Require (And Why DevOps Owns It)
Security logging and monitoring is required by SOC 2 and CMMC — and it sits squarely at the intersection of compliance and DevOps. Here's what both frameworks require and what your engineering team needs to own.
Least Privilege Access: The Control That Shows Up in Every Framework and Fails in Most Audits
Least privilege access is required by SOC 2, CMMC, and ISO 27001 — and fails in most audits. Here's what the control actually requires across frameworks and where organizations consistently fall short.